Trust and security
Where we store your company’s data, who can see it, and how to report a problem. This page is the short version; our policies are the full one.
- Data
- Stored in India
- Runs
- Our cloud, your cloud, on-premise or air-gapped
- Security
- security@lumiotech.io
Where your data is stored
- On the Lumiotech cloud, your data is stored in India.
- lumioCapital and lumioWhisper can run in your private cloud or on-premise instead, so records never leave your infrastructure.
- lumioWhisper can also run air-gapped, with no internet connection, answering from the sources you load.
Who can see what
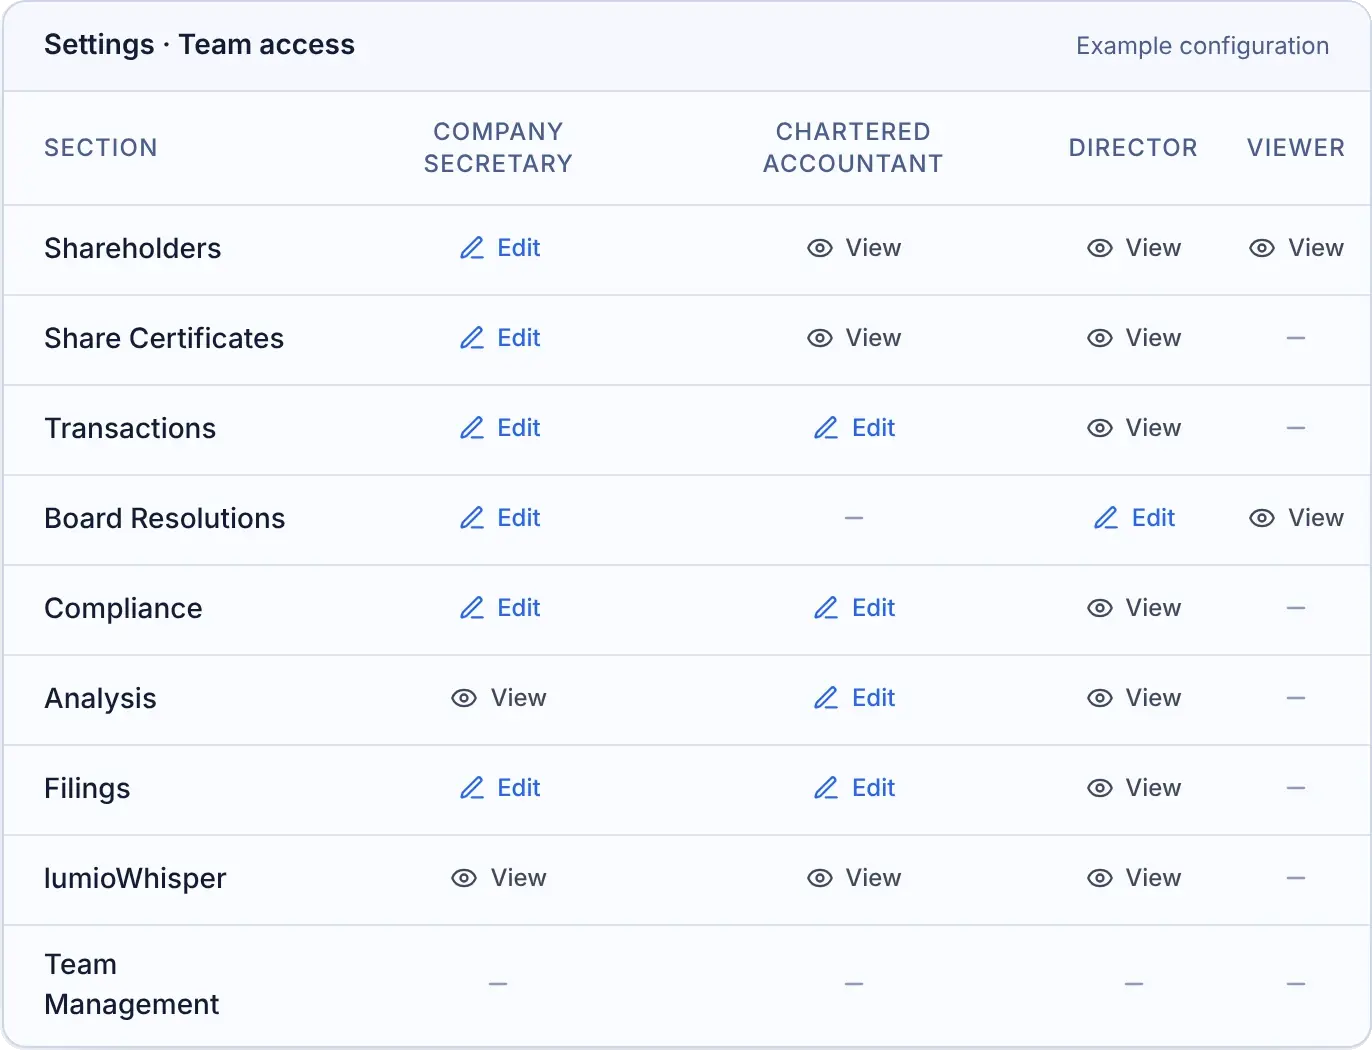
- Access is set by role. Founders, directors, company secretaries, auditors and recruiters see only the sections their role allows.
- lumioWhisper reads lumioCapital records only after the workspace owner approves the connection, and that access is read-only.
- Inside Lumiotech, access to customer data follows least privilege, is reviewed regularly and is logged.
How AI features use your data
- lumioWhisper cites the statute, circular, page or record behind each claim, so every answer can be checked.
- Questions and answers are kept in an audit trail.
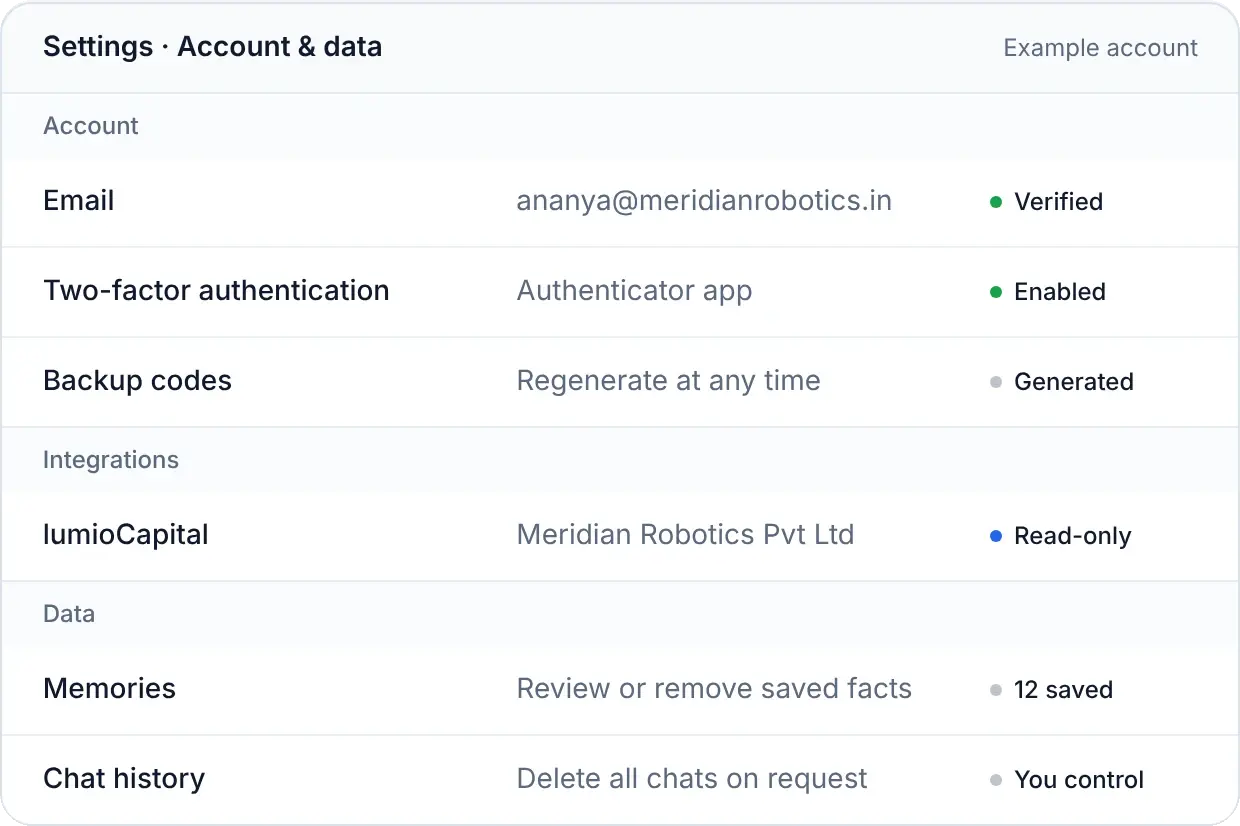
- Saved memory can be reviewed or removed in settings, and zero-data-retention options are available for regulated teams.
How data is protected
- Data is encrypted in transit with TLS 1.3 and at rest with AES-256.
- Accounts are protected with multi-factor authentication, session timeouts and login monitoring.
- Security logs are kept for 180 days, as CERT-In’s April 2022 directions require.
If something goes wrong
- Reportable cybersecurity incidents are reported to CERT-In within six hours.
- Affected customers are told what happened and what we are doing about it.
- Every incident ends with a review and tracked fixes.
Reporting a vulnerability
- Email security@lumiotech.io with what you found and how to reproduce it.
- Please give us reasonable time to fix the issue before telling anyone else about it.
- Our contact details are also published in security.txt.
Policies
The full terms. Questions about any of them go to legal@lumiotech.io.
- Privacy PolicyHow Lumiotech collects, uses, and protects personal information.
- Terms of ServiceTerms governing use of Lumiotech websites and platforms.
- Refunds PolicyRefund and cancellation terms for Lumiotech products and services.
- Security PolicySecurity practices and controls across Lumiotech platforms.
- Data ProtectionData protection commitments for enterprise and regulated customers.
- ComplianceThe standards and regulations Lumiotech products are built to meet.
Questions about security
Ask us about our security practices or a private deployment. We reply within one to two business days.